



As the trend in OT/IT convergence continues to grow, almost every industrial organisation has started reinforcing its network security and taking cybersecurity precautions to protect its operations. One of the main reasons for this is that critical infrastructure and manufacturing facilities are more likely to be targeted by cyberattacks. In addition to incurring financial losses when a company is hit by a cyberattack, if it makes the news, it will often lead to reputational damage as well. More companies are being targeted by ransomware attacks, and even some of the biggest players in the industry, who have already taken precautionary measures, are being targeted. These attacks demonstrate the high risk of an interconnected world, and that no organisation is immune from cyberattacks.
How to effectively implement cybersecurity measures without disrupting industrial operations OT environments is a complicated issue. There are many approaches and architectures that must be carefully considered before a decision can be made. In this article, we will explore two of the most common security architectures used now and share some tips to help industrial organisations implement them in unique OT environments.
The initial focus of zero trust architecture, as stated in the NIST Special Publication 800-207, is to grant only the minimum access privileges to those who need to operate on the network. This will prevent the situation when someone has a legitimate reason to access the network, but they are unnecessarily given unrestricted access to parts of the network that they do not require access to, which increases the chances of a cybersecurity breach occurring.
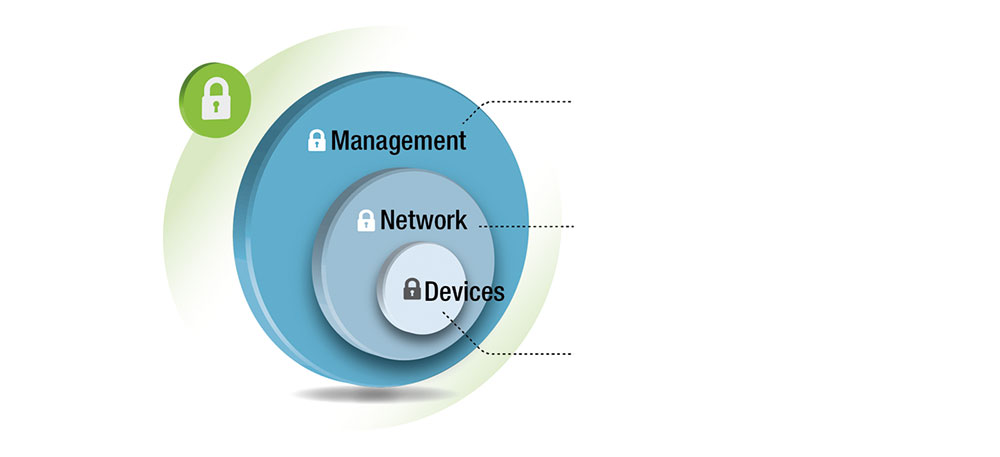
We will now consider the defence-in-depth approach, which contains multiple layers of security protection to reinforce network security for industrial operations. The rationale behind this is that you will have a second chance to protect zones and conduits if the first layer of protection fails. According to the IEC 62443 cybersecurity standard, it is necessary to start this process by partitioning areas based on the levels of protection required. Each partition is called a zone, and all the communication devices within it share the same security level, which means they all have the same level of protection. If you want to enhance security even further, it is possible to place a zone inside another zone with additional security measures.
By combining the two approaches that we have just considered, you can build well-defended industrial operations with layers of protection as the foundation, and then add further protection by adding the zero trust mechanism to ensure access is restricted to only those who need to access certain areas of the network. After considering these two approaches, it is clear there is no silver bullet for cybersecurity, and there are multiple angles that must be considered to ensure your network is secure.
One unfortunate scenario that is often seen on industrial networks is when user credentials are compromised. For networks that do not utilise the zero trust principle, a user’s credentials might be all a malicious actor needs to gain access to the network. However, for a network that utilises zero trust architecture, a malicious actor requires not only device access control, but also user authentication and authorisation. On top of that, it is also suggested to utilise trust lists for granular control of your network.
Device access control: By using trust lists, rate control and failure logout, network devices allow access only from trusted devices that are equipped with the secure boot function and prevent excessive attempts such as brute-force attacks.
User authentication and authorisation: By verifying the user’s credentials when logging on to devices, network devices will log all user access attempts and provide the lowest level of privileges based on the role of the user.
Trust lists: If organisations hope to reinforce security, trust lists can be a good way to control network traffic. One common practice is to create a trust list for IP addresses and service ports, and to leverage deep packet inspection technology to granularly control the network with features such as read or write privileges.
As a leader in industrial networking for 35 years, Moxa is committed to developing secure and reliable networking solutions that proactively identify and mitigate cyberthreats in OT environments. To realise this commitment, Moxa strictly follows secure-by-design practises to develop network devices with security features based on the IEC 62443-4-2 cybersecurity standard. The practical security features can help organisations realise zero trust networks. Moxa also utilises distributed OT intrusion prevention system capabilities, and industrial secure routers with OT deep packet inspection, to perfect defence in depth of industrial networks.
| Tel: | +27 11 781 0777 |
| Email: | [email protected] |
| www: | www.rjconnect.co.za |
| Articles: | More information and articles about RJ Connect |






© Technews Publishing (Pty) Ltd | All Rights Reserved
 printer friendly version