



A good SAM (secure access manager) solution is focused on delivering productivity gains for administrators and users while achieving the highest level of security and compliance in managing, securing and reporting on remote device access. A SAM solution addresses the need for secured remote access to remote field IEDs (intelligent electronic devices), for maintenance, configuration and data retrieval. The benefit of using a SAM, as opposed to standard remote access such as a VPN, is the added security and control it provides.
Authentication and encryption control
This type of solution allows a native IED application to communicate with its associated devices as if the user were connected directly to the remote device in the field. The SAM solution will provide control over the authentication and encryptions necessary and will create a transparent tunnel between the application and the IED, over almost any Ethernet infrastructure (LAN, MAN, WAN).
The overall solution will control user groups, individual users and their passwords, including password changing if required. Rather than an end user logging directly into an IED with the IED specific username/password combination, they will instead log into the SAM server using their unique username and password. Once authenticated to the SAM it will show a list of devices the user is allowed to connect to that have been configured by the solution administrator. The user can then select the device they want, as well as the application they wish to use to connect. These applications should be able to run off the user’s computer directly, or alternatively, the solution should support thin-clients, where the clients will not have the application installed directly, instead they will run it off the main server.
One of the benefits of running a SAM solution is that users do not have to remember a variety of different usernames and passwords for end devices, rather they just need their SAM username and password to connect to any device. Being able to control what devices a user is allowed to connect to, as well as the ability to log details such as login attempts on a per user basis, provides a much more secure network environment, one that is protected against accidental changes (if the user connects to the wrong end device without realising) or malicious changes (which can be enacted by a disgruntled or ex-employee that still has access to site).
Automated functionality
Extending the functionality that allows users to tunnel through the SAM to connect to an end device, a good SAM solution will also be able to automate certain routine functions, such as data/file retrieval and password/configuration management. This extends the benefits of using a good SAM solution from securely managing user access to reducing travel to remote sites for data retrieval and configuration management.
Once file and configuration retrieval from end devices is in place, the SAM can use intelligence to query these files and configurations and to compare them to existing master files. So, for instance, if the configuration of a unit is changed, either intentionally or accidentally, the SAM will detect that there is a mismatch between the devices configuration and the master for that device or device group. An alert can then be generated to relevant users who will be able to identify the changes using the SAM and either confirm or deny these. If confirmed the new configuration can be stored as the master, whereas if the change is denied the old master firmware can be re-uploaded to the device.
RuggedCom’s Crossbow SAM solution
The system will usually consist of a central server along with multiple users. These users will generally be the engineers PCs or laptops, running a client application to connect to the server. The server will contain the system database (e.g. based on SQL server), as well as storing all configuration files. Depending on the requirements, either the server can host the IED applications (thin-client scenario) or alternatively these can be hosted directly on the client machines.
As a SAM solution is used to provide remote access, a problem can occur if a station loses its link to the central location where the SAM server is stored. As the device passwords are unknown to the system users (this is automated by the SAM), loss of connectivity to the SAM can mean that the users are not able to log into the end devices. A good SAM solution will solve this dilemma by having redundant, partial functionality servers that are stored locally within each station, often known as SACs (station access controllers). Partial functionality means that although the user may not have the full intelligence and automation functions of the SAM available, they will still be able to login to end devices through the SAC and so are still able to troubleshoot and resolve problems. If a solution using SACs is considered, it is essential to make sure that the SAC applications are installed on servers that can handle the substation environments, as losing this SAC as well as connection to the SAM can cause problems. Often it is advised to install the SAC on an industrial or embedded PC that is rated for high EMI resistance.
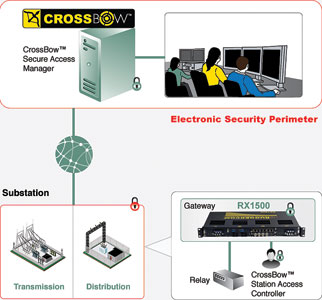
An example of RuggedCom’s Crossbow SAM solution topology is shown in Figure 1. As can be seen, the SAM is located in the control centre along with the various authentication servers if required. All communications to remote relay and RTUs will pass through the SAM, which will tunnel the connections from the clients in the control room to the remote end devices in the field. The RX1500 gateway supports an embedded industrial PC that can run the SAC, allowing access even if the uplink to the control centre is down. Typical SAM system benefits include:
* Individual user accounts and privileges.
* Strong authentication for users.
* Global password management of relays and gateway devices
* Configuration and firmware management of relays and gateway devices.
* Integrated file management provides controlled access, version control and history for all file types.
* Support for third party security event management systems.
* Blocking of specified IED command improves security and reduces errors.
* Automatic, scheduled retrieval of important IED event files.
* Preserves investment in legacy gateway devices and communication infrastructure.
* Administration tools supports management of thousands of IEDs and hundreds of users.
* Meets NERC CIP standards for cyber security.
* Integration with Active Directory, RSA SecurID and other enterprise authentication solutions.
For more information contact H3iSquared, +27 (0)11 454 6025, [email protected], www.h3isquared.com
| Tel: | +27 11 454 6025 |
| Email: | [email protected] |
| www: | www.h3isquared.com |
| Articles: | More information and articles about H3iSquared |






© Technews Publishing (Pty) Ltd | All Rights Reserved
 printer friendly version